What is vCluster?
vCluster is a solution that builds fully isolated Kubernetes environments “tenant clusters” on top of your existing infrastructure. Each tenant cluster has its own dedicated API server, with independent RBAC and CRDs, giving users an experience that is indistinguishable from having a dedicated Kubernetes cluster of their own. And crucially, no physical nodes need to be dedicated to a tenant cluster.
Since vCluster (formerly Loft Labs) the pioneer of Kubernetes virtualization released it as open source in 2021, the company has expanded its product line for AI and GPU infrastructure, and it is now widely adopted as foundational technology by AI cloud providers and AI factories worldwide. With more than 40 million tenant clusters deployed to date, it has become the de facto standard for Kubernetes multi-tenancy.
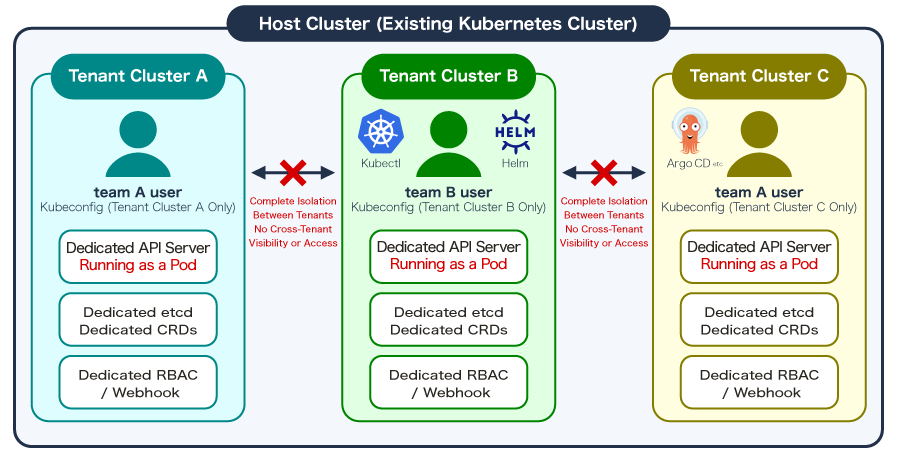
What does a tenant cluster look like?
From the perspective of users and workloads, a tenant cluster is a complete Kubernetes cluster in every respect. Each user receives a kubeconfig valid only for their own cluster, and can operate it using standard Kubernetes-compliant tools such as kubectl, Helm, Argo CD, and Crossplane. There is no way to reference or access other tenant clusters, or the underlying control-plane cluster.
From the platform operator’s perspective, however, the control plane of each tenant cluster is simply running as a single Pod within a namespace on the control-plane cluster. Creating a new tenant cluster requires no additional infrastructure whatsoever.
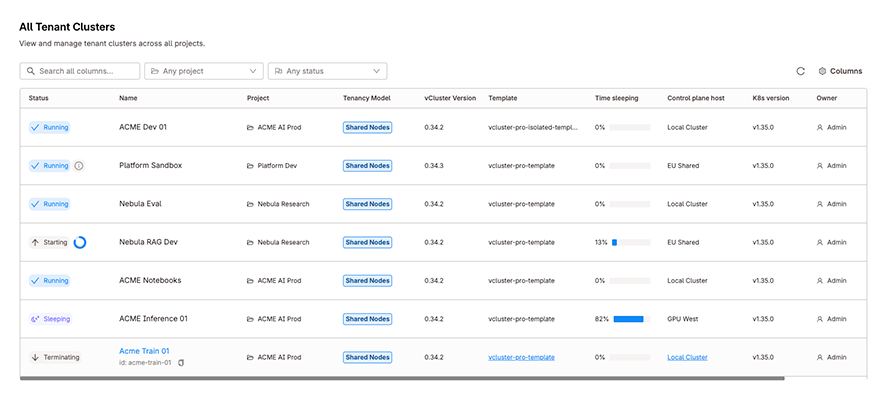
The tenant cluster dashboard gives operators a single screen to check the lifecycle status, project membership, applied templates, sleep state, and control-plane placement for every cluster.
Two isolation models
Every tenant cluster enforces strict isolation at the API level. Each tenant is assigned its own dedicated API server, its own dedicated etcd, and its own dedicated resource space, so resources created within one tenant cluster are never visible to another tenant. CRDs, admission webhooks, and RBAC policies are all scoped entirely within each tenant and never affect other tenants or the host cluster.
For workloads that require node-level isolation as well GPU infrastructure, regulated industries, or services delivered to external paying customers private node configurations are also supported. In this model, each tenant’s workloads run on dedicated compute resources, so no cross-tenant references occur even at the infrastructure level.
API-level isolation (standard)
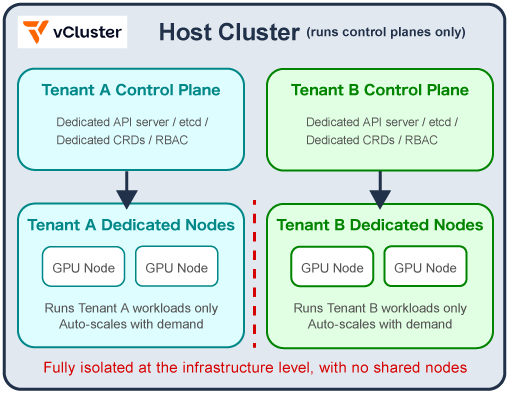
Use cases:
Internal team platforms, dev/CI environments, cost-efficient multi-tenant environments
Node-level isolation (private nodes)
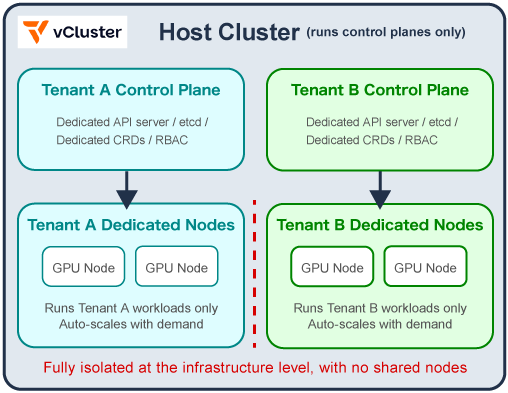
Use cases:
External-facing AI cloud / GPU-as-a-Service offerings, regulated industries, sensitive workloads
What is vCluster Platform?
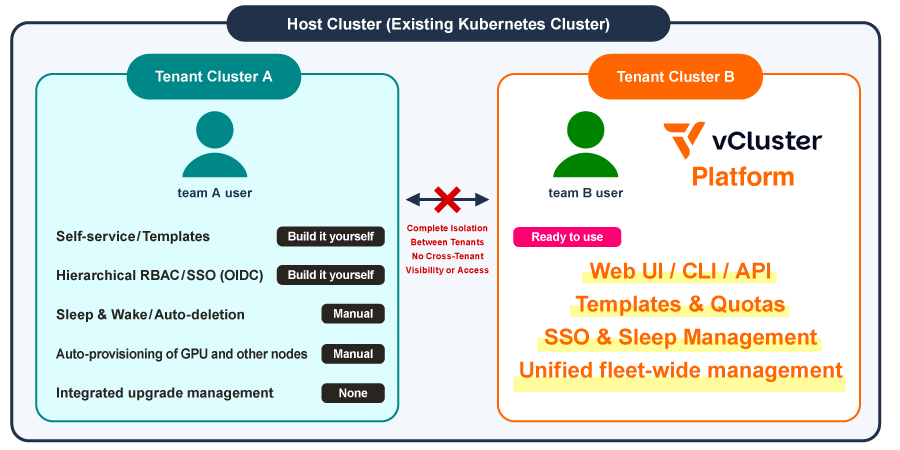
vCluster Platform is the management plane for your entire fleet of tenant clusters. Through a web UI, CLI, and API, it lets you deploy, configure, and operate tenant clusters across one or more control-plane clusters*¹. Access control, lifecycle automation, resource governance, and node management are all built in as standard features.
vCluster alone is enough to create virtual clusters. But once you’re running dozens or thousands of tenant clusters as an organization or a business, questions inevitably arise: Who is allowed to create which clusters? What are the resource limits? Who cleans up abandoned clusters? Who handles version upgrades, and when? Covering all of this indefinitely with in-house scripts and operational rules is not realistic.
vCluster Platform comes with built-in provisioning, access control, quota, and lifecycle management mechanisms, replacing your homegrown operational tooling entirely with a production-ready management layer. Pacific Teck is the only company providing sales and Japanese-language support for vCluster Platform in Japan.
*¹ Control-plane cluster:
A Kubernetes cluster that hosts the virtualized control planes of tenant clusters. The control-plane cluster is operated by the platform provider and is never visible to tenants. There is no sharing of control-plane nodes, no in-cluster agent Pods, and no lateral path between tenant environments. In a shared-node configuration, tenant workloads run alongside control-plane Pods on this same cluster both share the same node pool.
Managing tenant clusters with the Platform
vCluster Platform is the management layer that governs your entire fleet of tenant clusters. Its responsibilities include:
| Provisioning | Create tenant clusters from the UI, CLI, or API. Use templates to enforce a baseline configuration across all clusters |
| Access control | RBAC at the platform, project, and cluster levels, plus SSO integration with any OIDC provider |
| Lifecycle management | Sleep, wake, auto-deletion, and version upgrades, orchestrated across the entire fleet |
| Multi-cluster | Manage tenant clusters spanning multiple control-plane clusters from a single Platform instance |
vCluster vs. vCluster Platform
| vCluster | vCluster Platform | |
|---|---|---|
| Create and run tenant clusters | ○ | ○ |
| Management method | CLI, Helm, etc. (per cluster) | Web UI, CLI, API (fleet-wide) |
| Self-service / templates | — (build it yourself) | ○ |
| Sleep & wake / auto-deletion | ─ | ○ |
| Hierarchical RBAC / SSO (OIDC) | — (build it yourself) | ○ |
| Automated provisioning of GPU and other nodes | ─ | ○ (private nodes) |
| Centralized multi-cluster management | ─ | ○ |
| Unified upgrade management | ─ | ○ |
| Support | Community | ○ (with Pacific Teck Support) |
Key use cases
AI cloud / GPU-as-a-Service providers
Map projects to customer accounts, with automatic GPU node autoscaling per tenant
Enterprise internal platforms
Team-level isolated Kubernetes environments with quotas and cost visibility
Research institutions & universities
Self-service clusters per lab or project on shared HPC/AI infrastructure
Development / CI environments
Ephemeral, disposable clusters with automatic sleep and auto-deletion
Get a quote for vCluster Platform
Pacific Teck provides Japanese-language pre-sales and post-sales support for vCluster across the Asia-Pacific region.
For inquiries, please contact us by email at info@pacificteck.com
PARTNERS